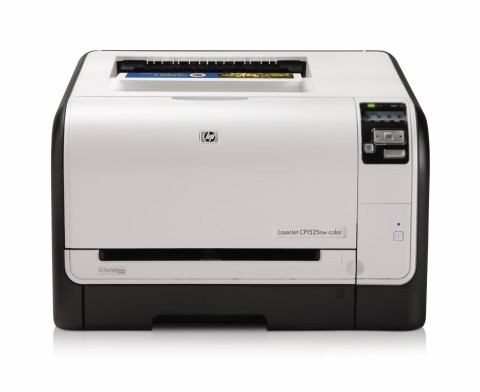
Three days ago, we brought you news
of how researchers have made proof-of-concept attacks on HP printers by
reprogramming their firmware. Among other things, these attacks could
deliberately cause the fuser in a printer to overheat and singe the
paper, until shut down by a built-in unoverridable thermal switch,
preventing a fire. Now, in light of this, a lawsuit has been filed by
David Goldblatt of New York, seeking damages for fraudulent and
deceptive business practices and is looking for class action status: "As
a result of HP's failure to require the use of digital signatures to
authenticate software upgrades, hackers are able to reprogram the HP
Printers' software with malicious software without detection," the suit says. "Once
the HP printers' software is maliciously reprogrammed, the HP printers
can be remotely controlled by computer hackers over the Internet, who
can then steal personal information, attack otherwise secure networks,
and even cause physical damage to the HP printers, themselves." Note
that HP has used digital signatures since 2009 to authenticate the
firmware updates, helping to mitigate this potential problem in recent
models.
Despite this though, HP still intends to patch the firmware to eliminate
threats from this hack, which exploits bugs in the firmware. As these
attacks have only actually been demonstrated in the lab and no actual
losses have been incurred by Goldblatt, it makes one wonder if he is
just using the prevailing American "victim culture" to try and make a
quick buck off HP. HP are the top printer brand, mainly because their
products are excellent, performing well and lasting a long time, plus
other companies' printers and embedded devices have the same problems,
so it seems unlikely that he would really not have bought HP printers.
Source: c|net
Showing posts with label HP. Show all posts
Monday, December 12, 2011
Friday, December 9, 2011
Hackers Can Make HP Printers Catch Fire!! Well, Singe Paper
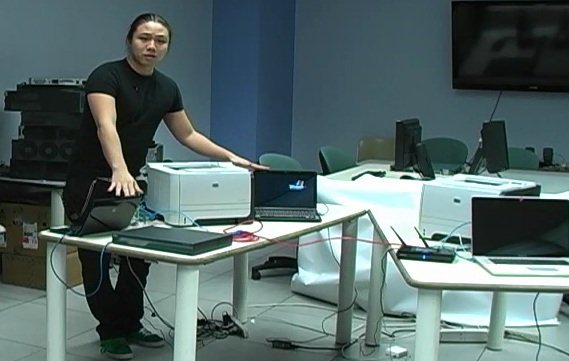
Researchers at Columbia University have investigated the security of HP
network printers and have found them wanting. The basic problem is the
complexity of the devices and the fact that the authenticity of firmware
updates for these devices isn't checked by using a digital signature.
MSNBC published an exclusive story,
explaining how by using a hacked computer, the researchers could make
their test printers do various nasties, such as continuously heat the
fuser unit until the paper singed, at which point the printer shut off
due to the built-in safety device, a thermal switch which cannot be
overridden by software. They could also be programmed to spread viruses,
which would be very dangerous, as these attacking printers would be
within the firewall perimeter, allowing them unrestricted access to the
soft underbelly of the network. And as the MSNBC article put it so well:
"Few companies are prepared to protect themselves from an attack by their own printer."
Quite, seems ridiculous at first sight, doesn't it? The researches
focused on HP printers, which are by far the most popular brand out
there, but say that there are similar vulnerabilities within all devices
which employ embedded networked computers, leaving them wide open to
attack, hence the industry should wake up to this threat and fix their
systems before hackers start to exploit these for real. HP for their
part, played down the overall threat and disagreed on several points
made by the researchers. Also, the attacks were carried out using Linux
and MAC
computers and the suggestion seems to be that it's somehow harder to do
with a Windows computer. There's a lot more detail at the MSNBC article
and readers are encouraged to check it out.
Subscribe to:
Posts (Atom)